The Proven Confidence of
INTEGRATED SASE
Integrated SASE frameworks delivering verified, industry-leading performance, year-on-year
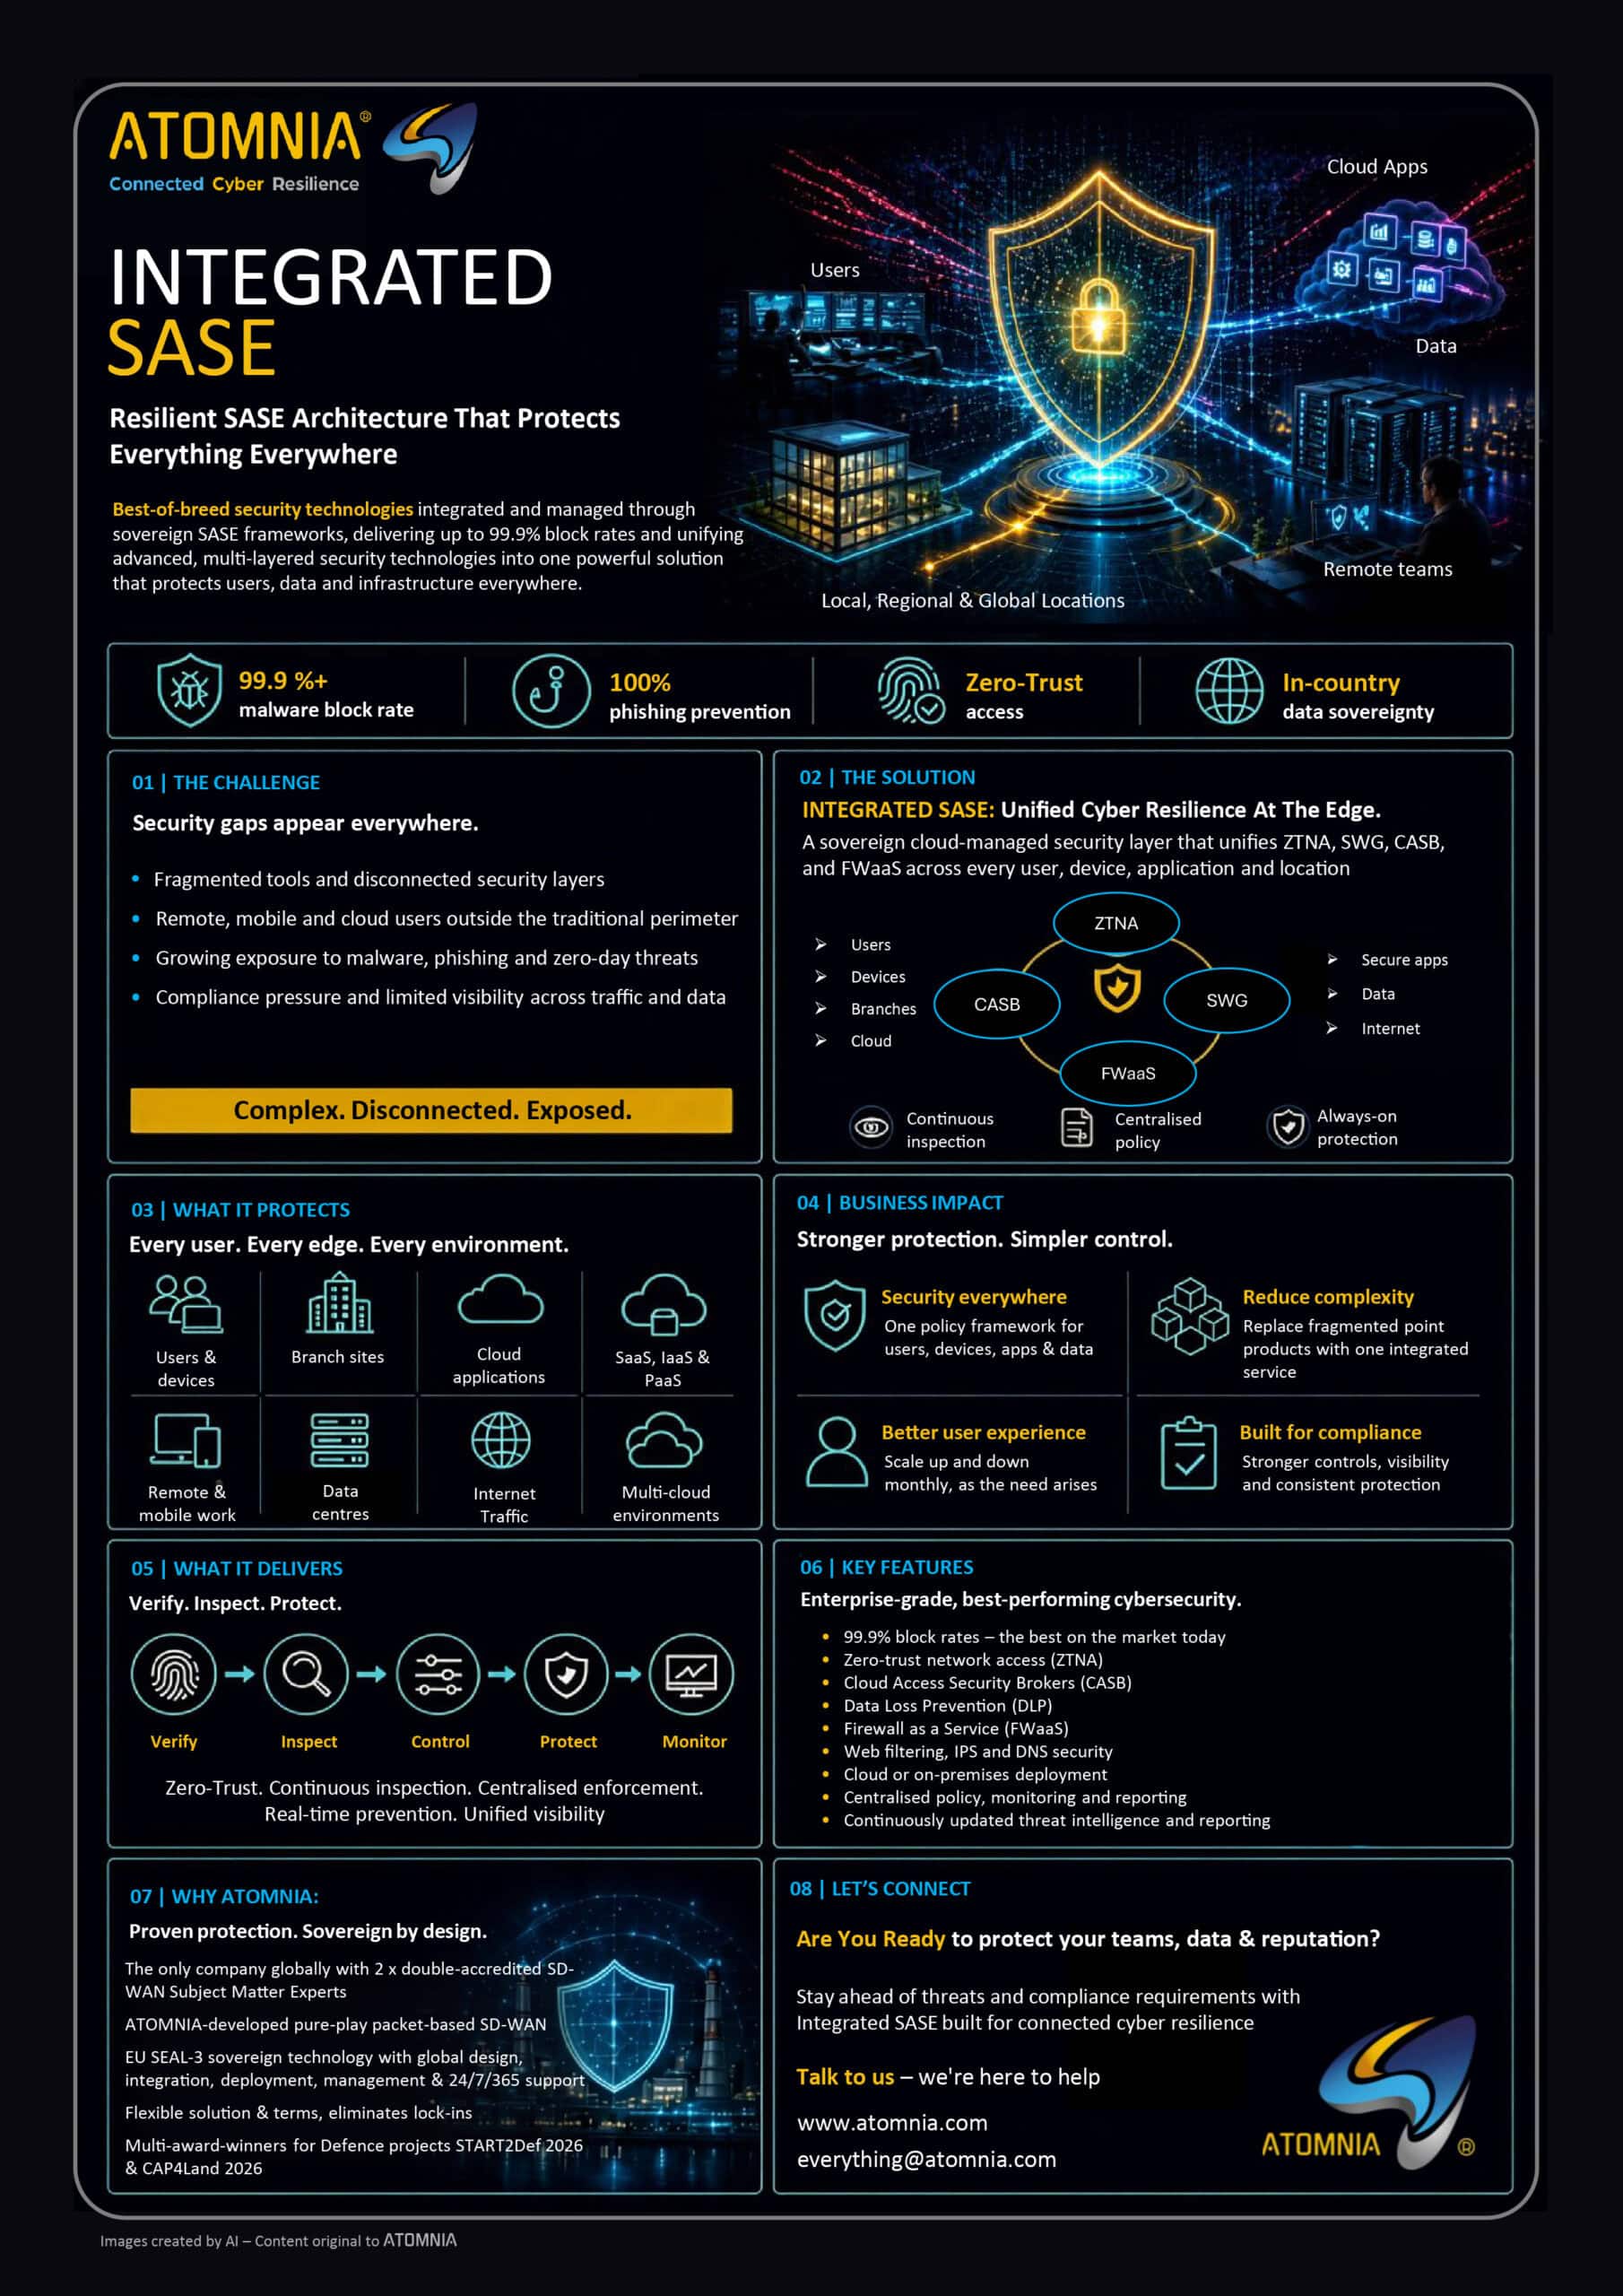
INTEGRATED SASE brings zero-trust access, secure web gateways, cloud application controls and firewall protection together to secure users, devices and data wherever work happens. Continuous inspection, data loss prevention and regularly updated threat intelligence help defend against evolving threats, while centralised policies keep protection consistent across branches, remote teams and cloud environments. Your IT team gains unified visibility and control, helping reduce security gaps and support compliance without juggling disconnected tools.
One integrated shield for connected cyber resilience
Integrated SASE brings security and network access together within OMNIA, helping protect users, devices, sites and cloud applications through one connected approach.
Security Everywhere
Protect users, devices, branch sites and cloud applications with consistent policy enforcement across your entire digital environment
Reduced Complexity
Replace fragmented point products and disjointed security layers with one unified framework that’s easier to manage
Cloud, Edge or On-Prem Flexibility
Deploy Integrated SASE in the way that best fits your business, whether at the edge, in the cloud, on-premises, or across a hybrid environment
Always-On Protection
Defend against malware, phishing, malicious URLs, command-and-control activity and zero-day threats with continuous inspection and prevention
Better User Experience
Give teams secure, seamless access to business applications and data without the friction, bottlenecks and poor performance of legacy security models
Centralised Visibility and Control
Monitor, manage and enforce security policies across users, locations and traffic flows from one place
Built for Compliance
Strengthen your security posture and support regulatory requirements with stronger controls, tighter visibility and more consistent protection
Scalable for Growth
As your users, sites and cloud services expand, Integrated SASE scales with you without forcing a patchwork of extra tools
Stop Managing Security Silos and Start Closing the Gaps
When work has moved beyond your security perimeter
- Remote teams and cloud applications need consistent protection
- Separate security tools leave policies, monitoring and reporting fragmented
- You need stronger access controls and data protection across users, devices and locations
Why INTEGRATED SASE is Different
More security tools shouldn’t mean more security silos. INTEGRATED SASE combines best-of-breed technologies within a sovereign security framework, bringing access controls, threat prevention and data protection together as one managed service. Rather than stitching separate products together, your team works through centralised policy, monitoring and reporting. Cloud or on-premises deployment, in-country data sovereignty and monthly scaling give you flexibility to match protection to operational needs, data requirements and changes in demand.
More layers of protection. Fewer layers of complexity.
View Technical Specifications
INTEGRATED SASE
Brief Technical Sheet
INTEGRATED SASE in OMNIA is the unified security layer that wraps SD-WAN and cloud access in a full SASE/SSE stack: ZTNA, SWG, CASB and FWaaS. It is built on best-of-breed Check Point technology, with in-country cloud gateways for data sovereignty and 99.9%+ threat blocking effectiveness.
| Area | Technical specification |
| Platform | Cloud-native SASE platform that unifies Zero Trust, Secure Web Gateway, CASB and cloud firewall in one integrated security layer for OMNIA. |
| Coverage | Protects users, devices, applications and data on-site, remote, mobile and across multi-cloud environments through a single policy framework. |
| Service options | Supports full SASE (SD-WAN + SSE) and pure SSE, depending on network architecture and use case. |
| Security framework | ZTNA, CASB, SWG, DLP and FWaaS provide multi-layered protection against current threats and zero-days. |
| Zero Trust | Enforces “never trust, always verify” across users, devices and applications, with least-privilege access to cloud and private applications. |
| Web security | Cloud or on-premises SWG filters user-initiated internet traffic, including URL and content filtering, malware and threat detection/prevention, DLP, and SIEM, SOAR and EDR integration. |
| Cloud security | CASB enforces enterprise security policies between users and SaaS, IaaS and PaaS services, providing compliance, visibility, threat protection and data protection. |
| Firewall security | Cloud-delivered next-generation firewall capabilities, including web filtering, advanced threat protection, IPS and DNS security, centrally managed as a service. |
| Data sovereignty | Purpose-built in-country OMNIA gateways and data centres keep traffic and logs within required jurisdictions for sovereignty and compliance. |
| Architecture | Cloud-native design with regional PoPs for low-latency inspection and policy enforcement close to users and applications. |
| Management | Centralised console for policy creation, monitoring and reporting across SASE components. |
| Operations | Distributed architecture designed for always-on security and high availability; scales for new users, locations and applications without additional hardware roll-outs. The cloud service is continuously updated with threat intelligence and features. |
| Threat prevention | Check Point-backed security with 99.9% malware block rate and 100% phishing/malicious URL prevention, based on Check Point independent tests. |
Deployment Models
- Cloud-based SASE/SSE via ATOMIUS Cloud gateways.
- On-premise security on VENA/VECTA SD-WAN appliances at the edge.
- Hybrid models combining centralised gateways, edge security and cloud enforcement.
- Centralised firewall architectures for legacy scenarios.
- Edge security on VENA/VECTA uCPE with SD-WAN and security.
- Cloud-based security through SD-WAN integration with cloud security providers.
Security Assurance
Check Point follows security-by-design principles using STRIDE-based design reviews, separate development, test and production environments, and continuous vulnerability tracking. Product hardening includes static code analysis, manual review, red-team testing and penetration testing. Supporting Check Point products comply with SOC 2, ISO/IEC 27000, Common Criteria, FIPS 140-2, NSS Labs, ICSA Labs, NIAP and CSfC, among other standards and schemes.
ARE YOU READY TO PROTECT YOUR TEAMS, DATA & REPUTATION WITH ONE POWERFUL CYBERSECURITY FRAMEWORK?